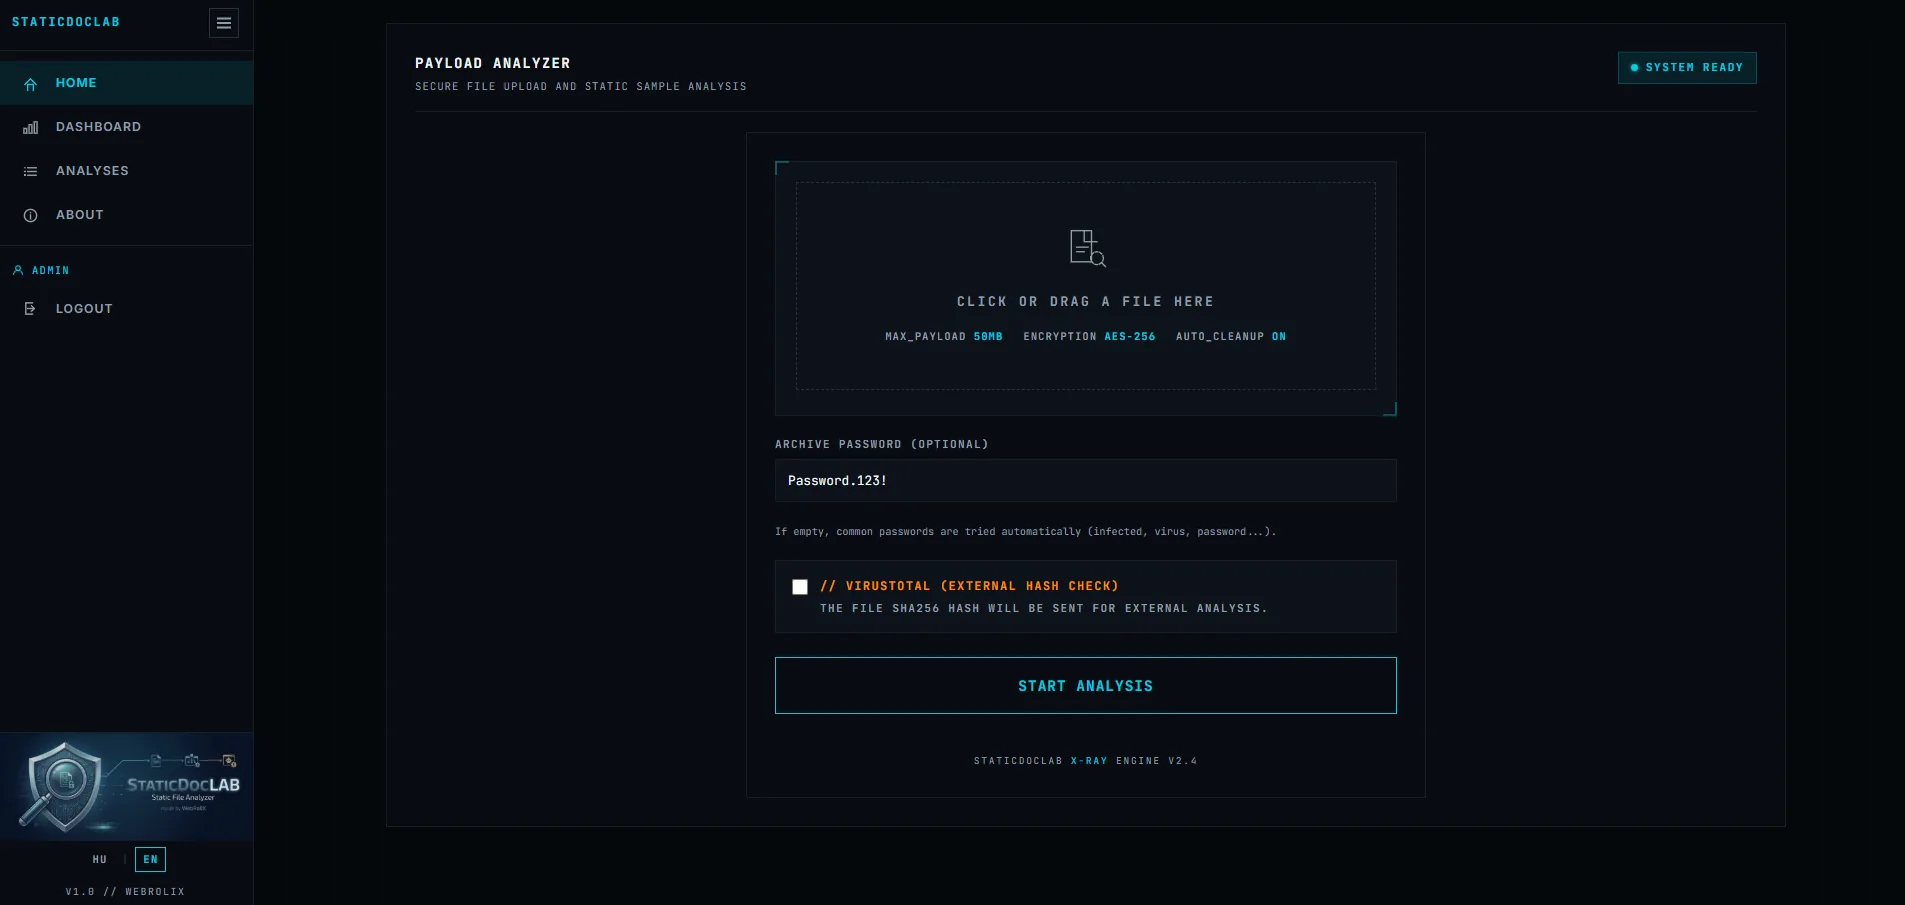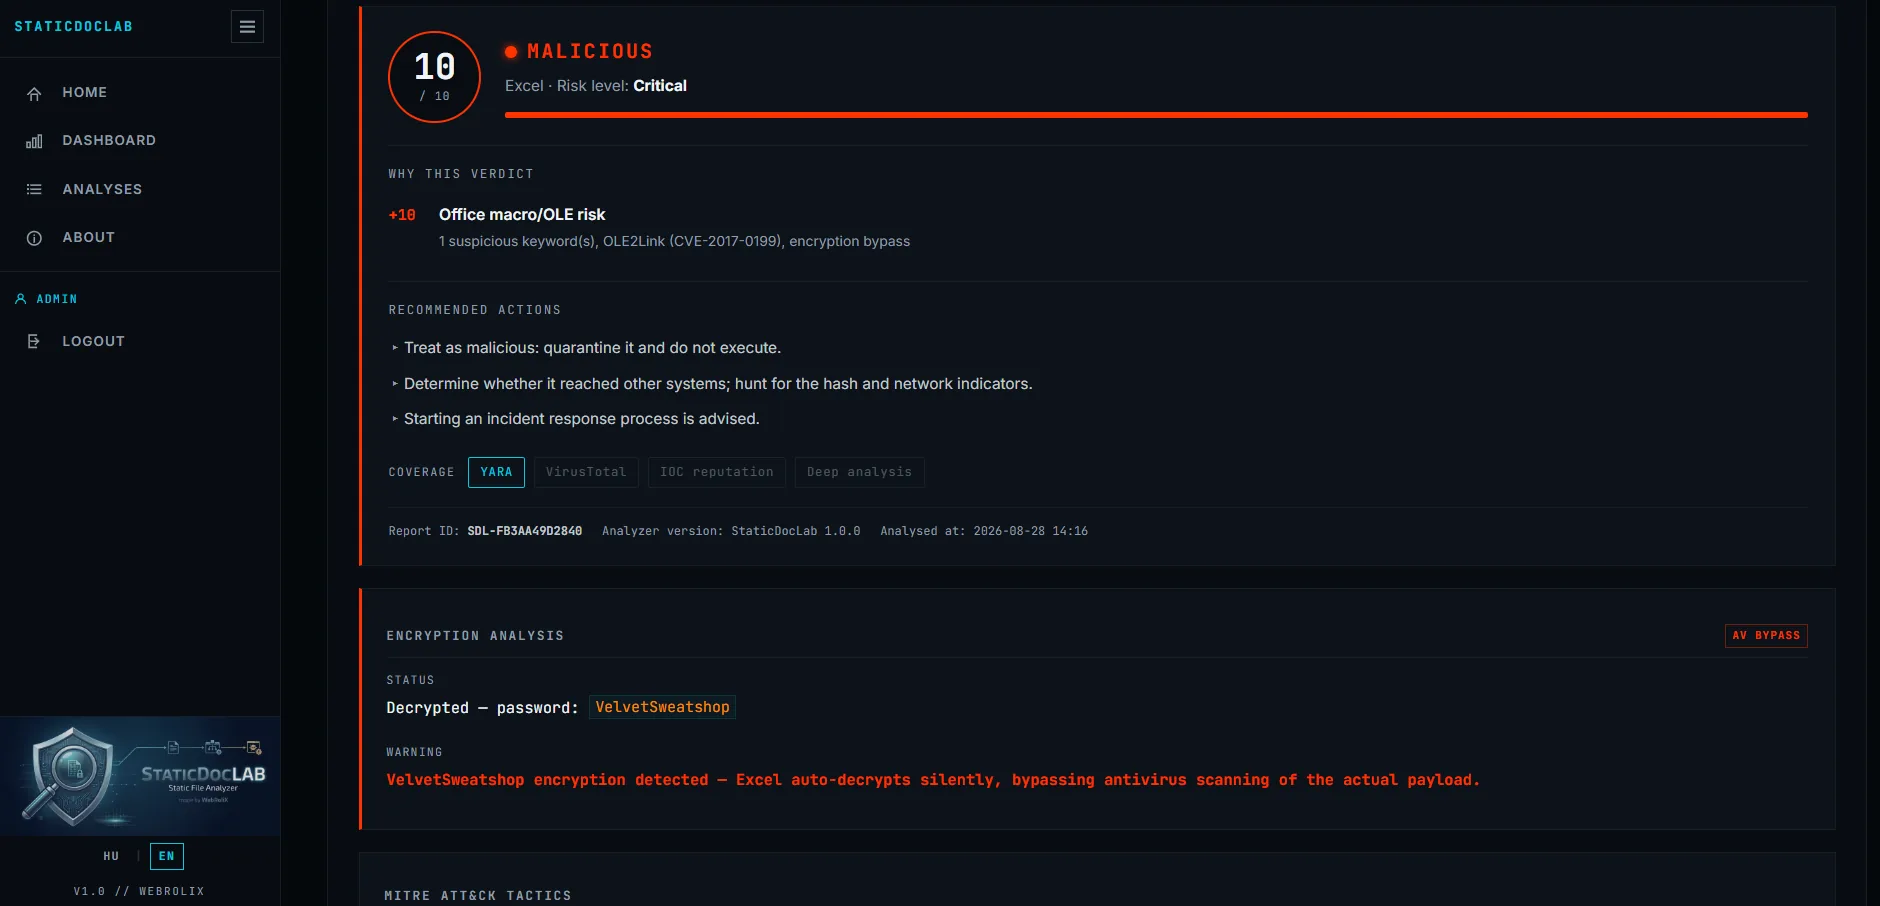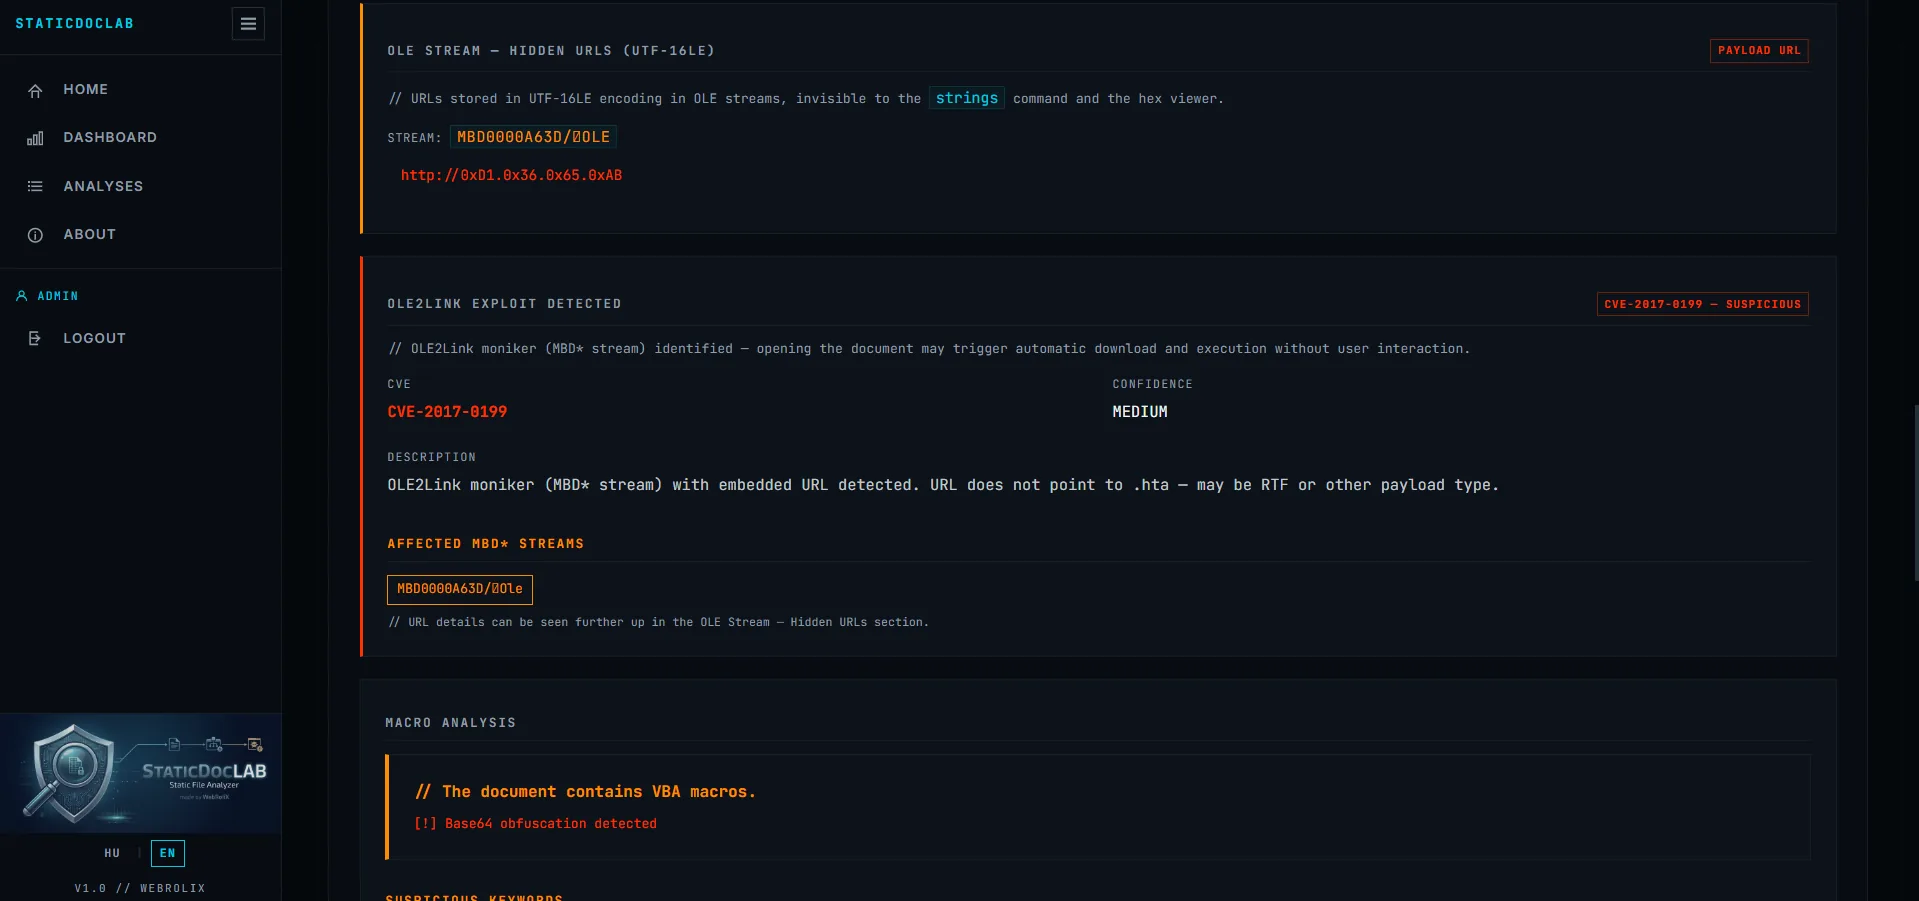
StaticDocLab
Fast static analysis of the files you receive every day. An extra line of defense, no sandbox, on your own infrastructure.
StaticDocLab sorts every incoming document, archive and attachment into one of five risk levels and, before anyone opens it, tells you: safe to open, or do not open. The file never has to run.
It is a Django-based, self-hosted platform for deep examination of PE, ELF and Mach-O binaries, PDF and Office documents, emails, archives, disk images, and LNK, HTML, SVG, CHM, OneNote and MSI files. A YARA rule engine, ClamAV, entropy analysis, static macro behavior analysis, CAPA and FLOSS deep scan all work together.
Findings are mapped to the MITRE ATT&CK framework automatically, and every file gets a risk score. Results export to PDF, JSON and CSV, and integrate into other systems over a REST API.
Key features
- PE, EXE, DLL and SYS deep analysis. Sections, import and export tables, entropy, suspicious API calls, signature verification.
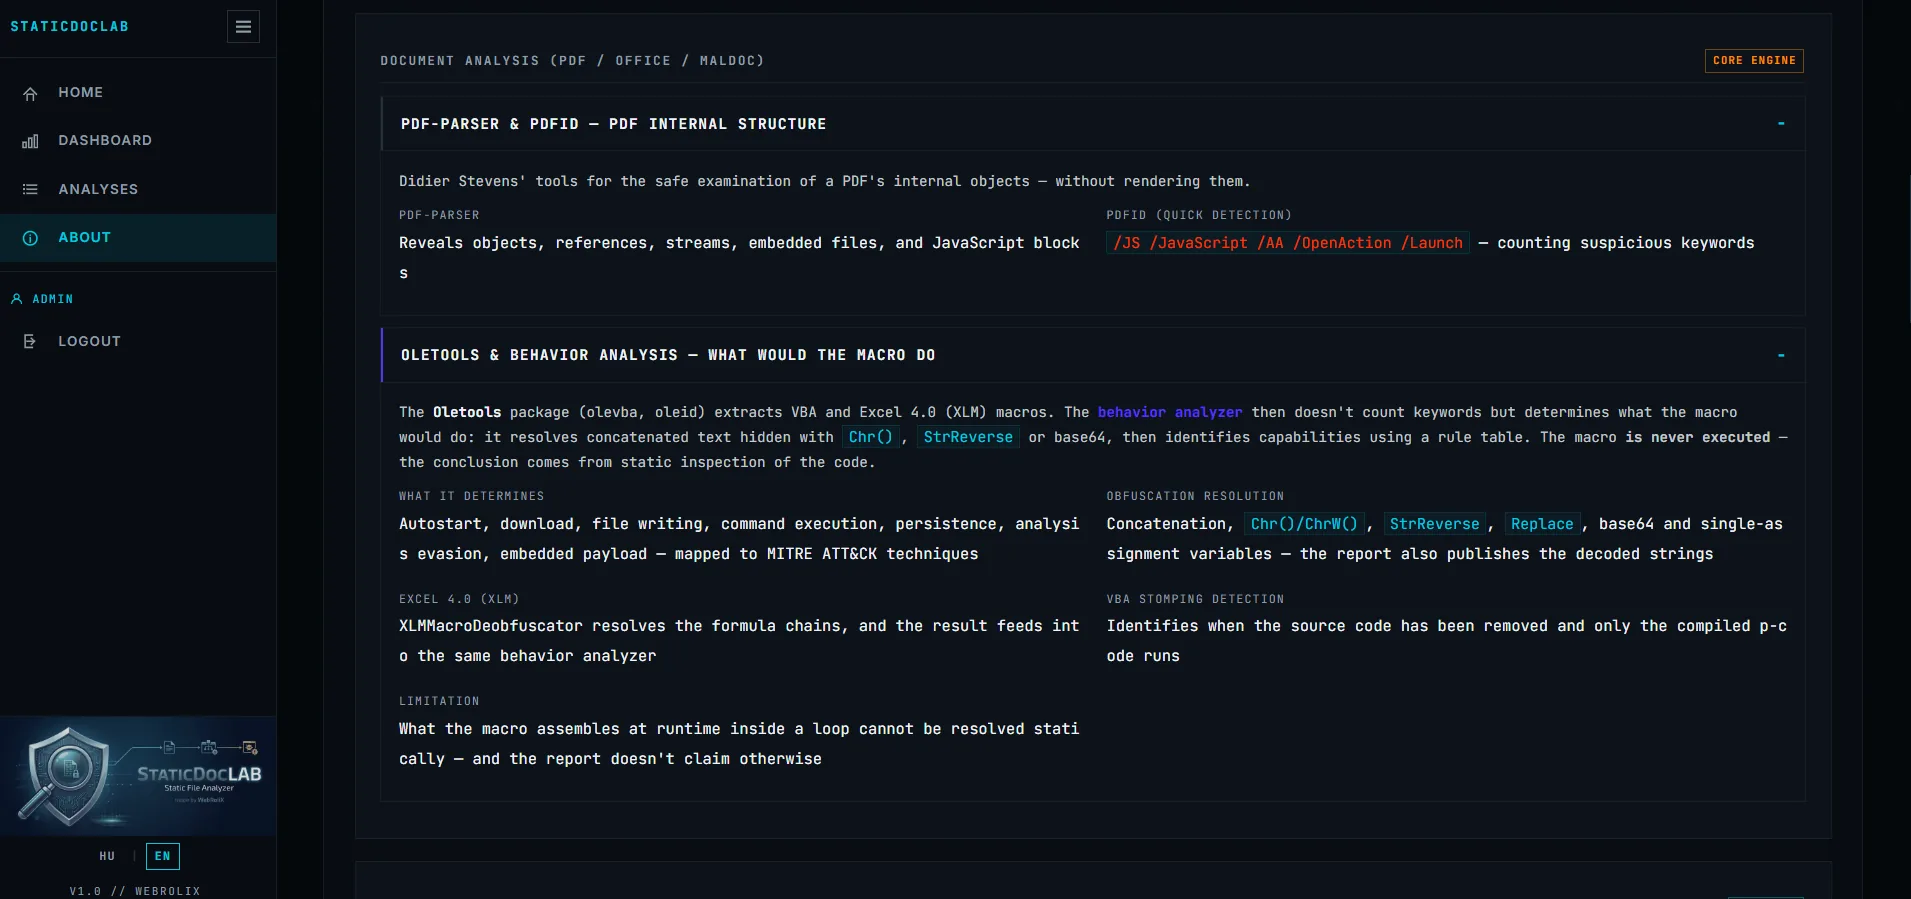
- PDF inspection. JavaScript and OpenAction detection, embedded file extraction, URLs from annotations, entropy analysis.
- PDF signatures and provenance. E-signatures (pyHanko) checked against EU trusted lists, C2PA content credentials against the official list.
- Office, OLE and RTF analysis. Macro behavior without running the macro (download, execution, persistence), XLM macros and VBA stomping.
- PowerShell decoding. Base64-hidden commands decoded recursively, plus what they would do: download, persistence, weakening defenses.
- Named attack techniques. Follina, Equation Editor, OLE2Link, the WinRAR CVE-2023-38831 flaw, remote template injection and MotW bypass.
- More file types. LNK command lines and LOLBAS, HTML smuggling, active SVG content, ISO and VHD disk images, MSI, CHM and OneNote.
- Email analysis from .eml and .msg. Header and metadata inspection, recursive attachment extraction, automatic IOC extraction.
- YARA rule engine. One-click updates from ten GitHub sources, custom rule upload and weighted risk scoring.
- Threat intelligence. VirusTotal, AlienVault OTX, AbuseIPDB, URLhaus, MalwareBazaar, offline ClamAV, ssdeep similarity, encrypted API keys.
- Linux ELF analysis and archive handling. Recursive ZIP, RAR, 7z and TAR extraction with password guessing and zip bomb protection.
- Export and REST API. Bilingual PDF report, JSON and CSV export, a token-based API with Swagger docs, duplicate hash detection.
> SCREENSHOTS
What it looks like in practice