LogStalker
Rapid investigation of event logs from compromised or suspicious Windows workstations and servers.
Anyone who has ever analyzed Windows event logs knows what endless work it is to go through several hundred kinds of events by type, without full knowledge of the case, find the connections between them, build the timeline and confirm the findings. This is where LogStalker comes in.
No more event log analysis that drags on for days. In minutes you find the traces of the attack, build the timeline systematically and collect the IoCs.
If the attacker is still inside your own infrastructure, fast and effective analysis is critical, because it can reduce the chances of lateral movement or further infections. It may also reveal the scope and nature of the compromise, so the attacker's traces can be unearthed more quickly.
Key features
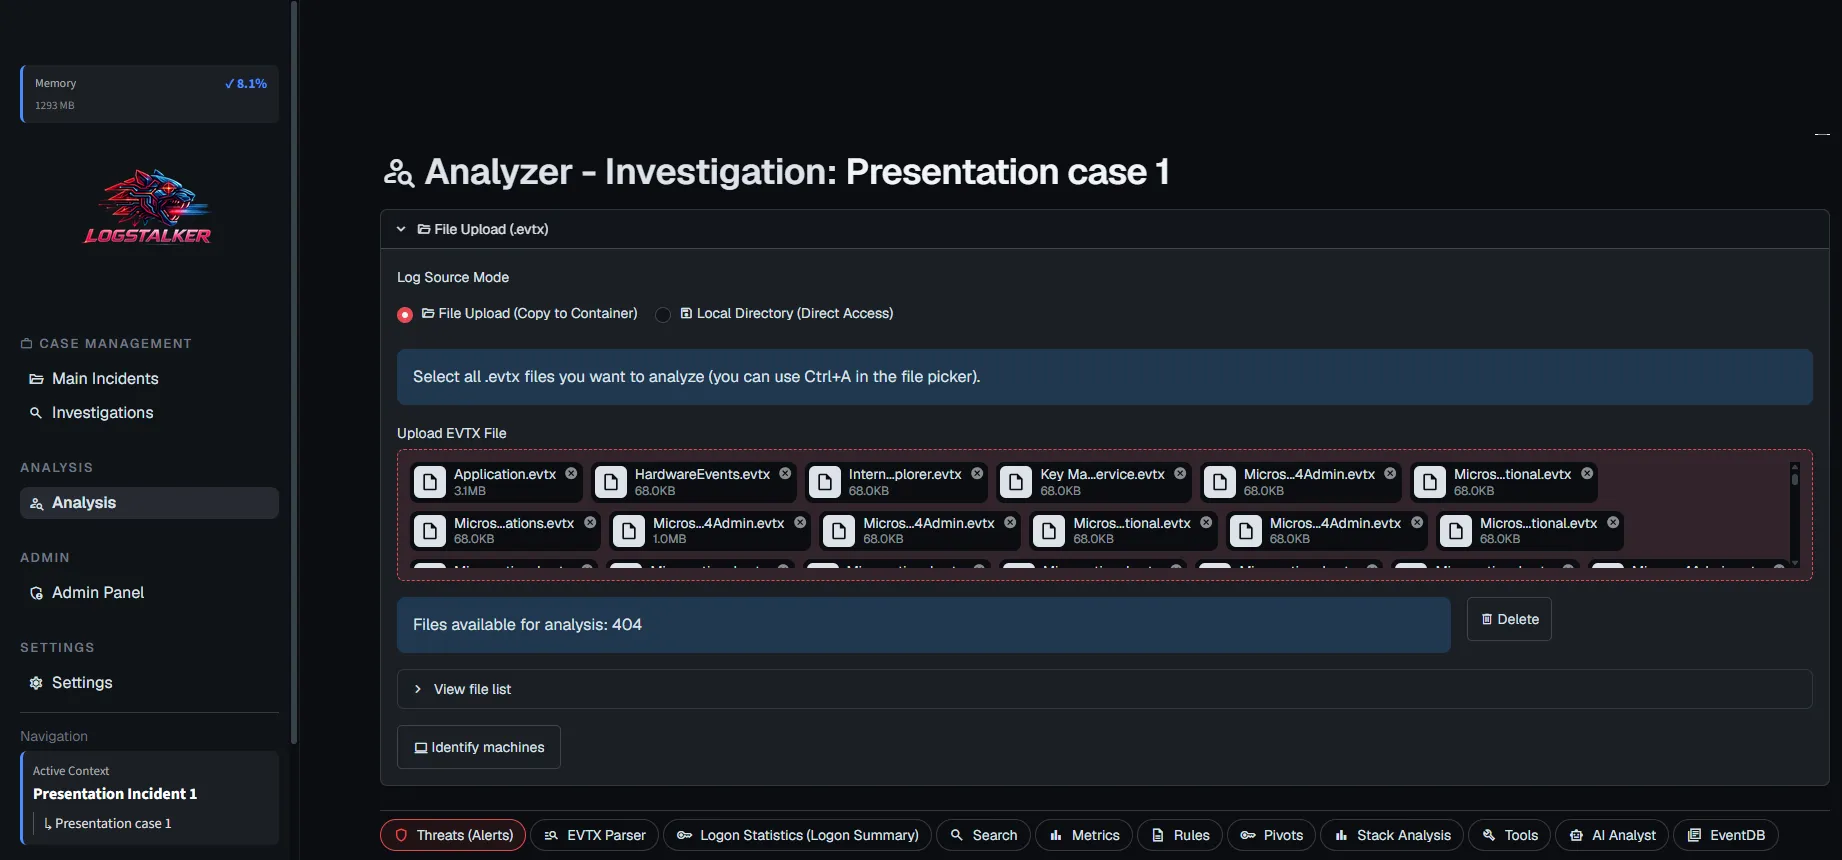
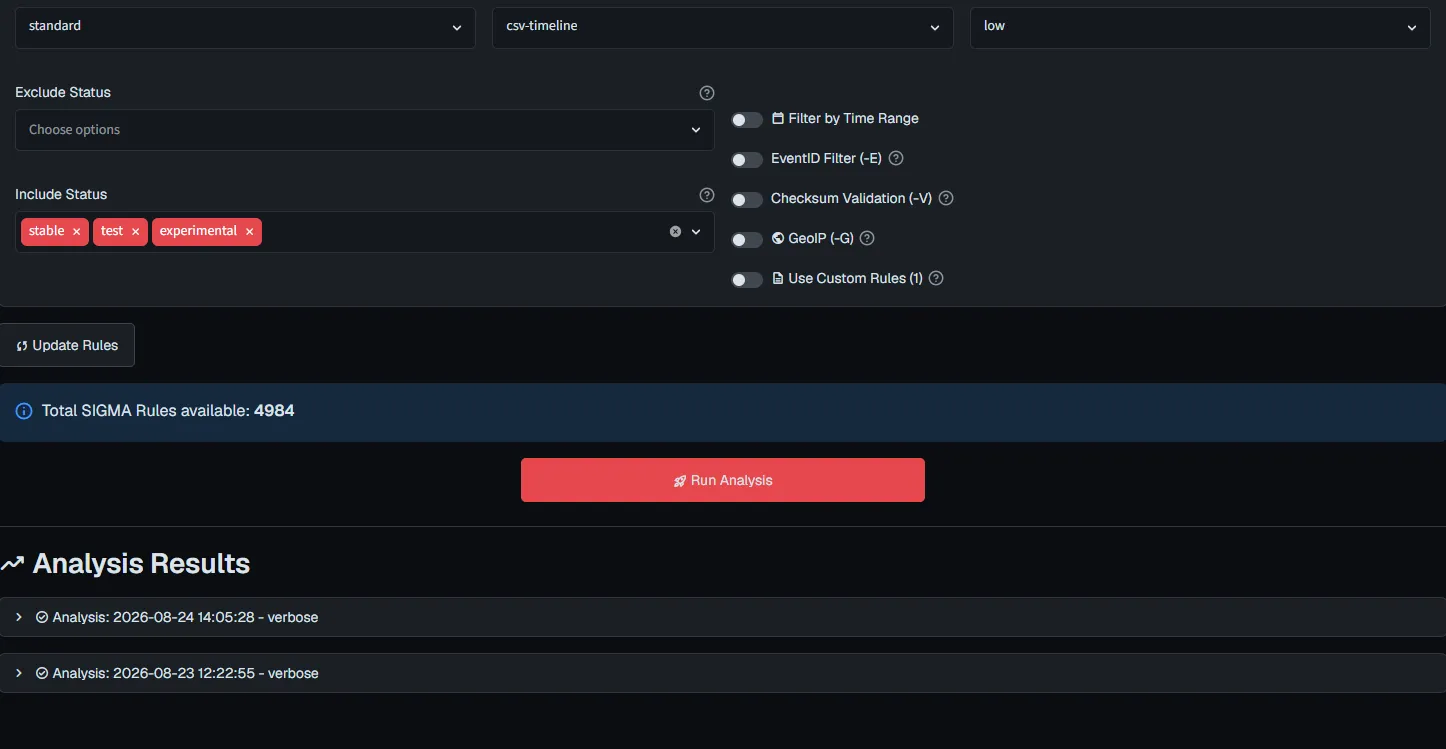
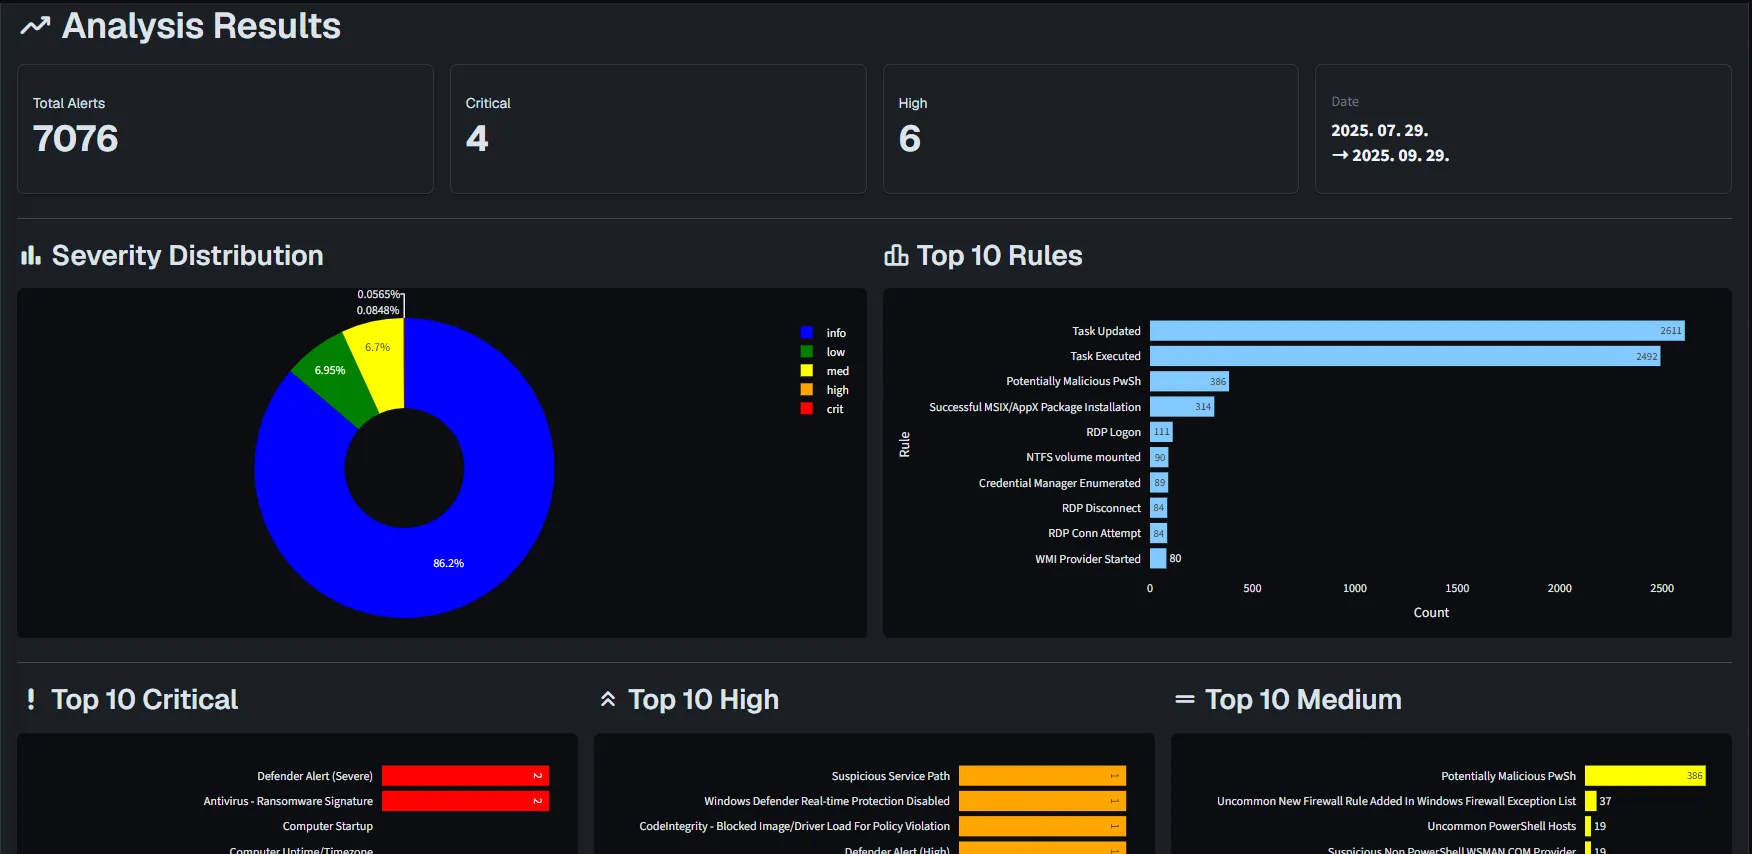
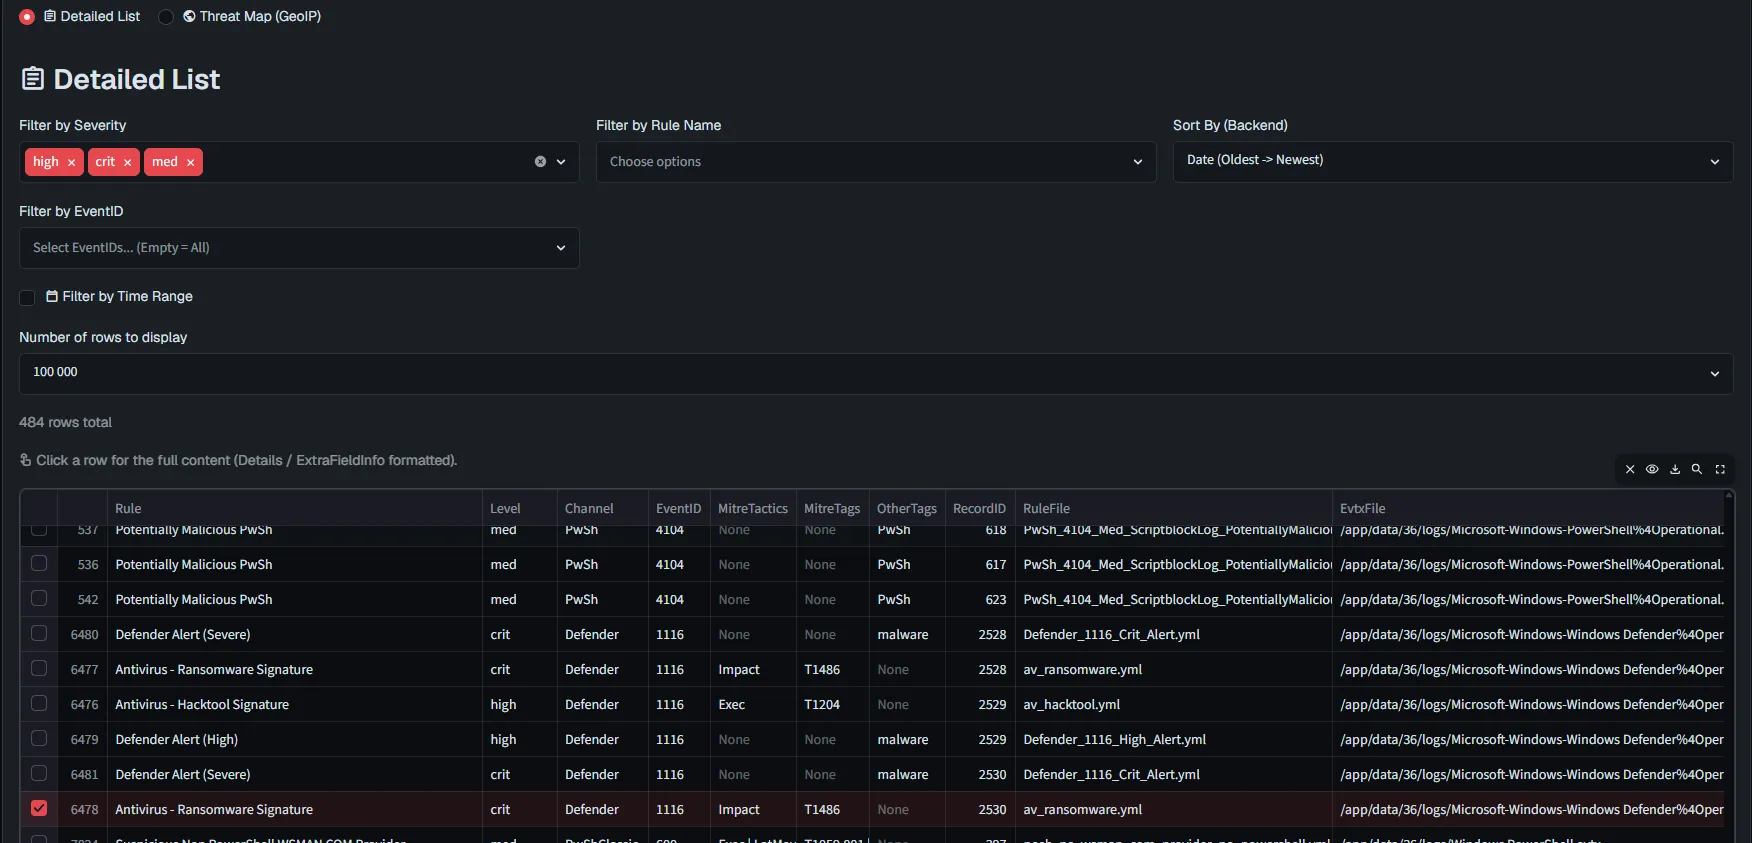
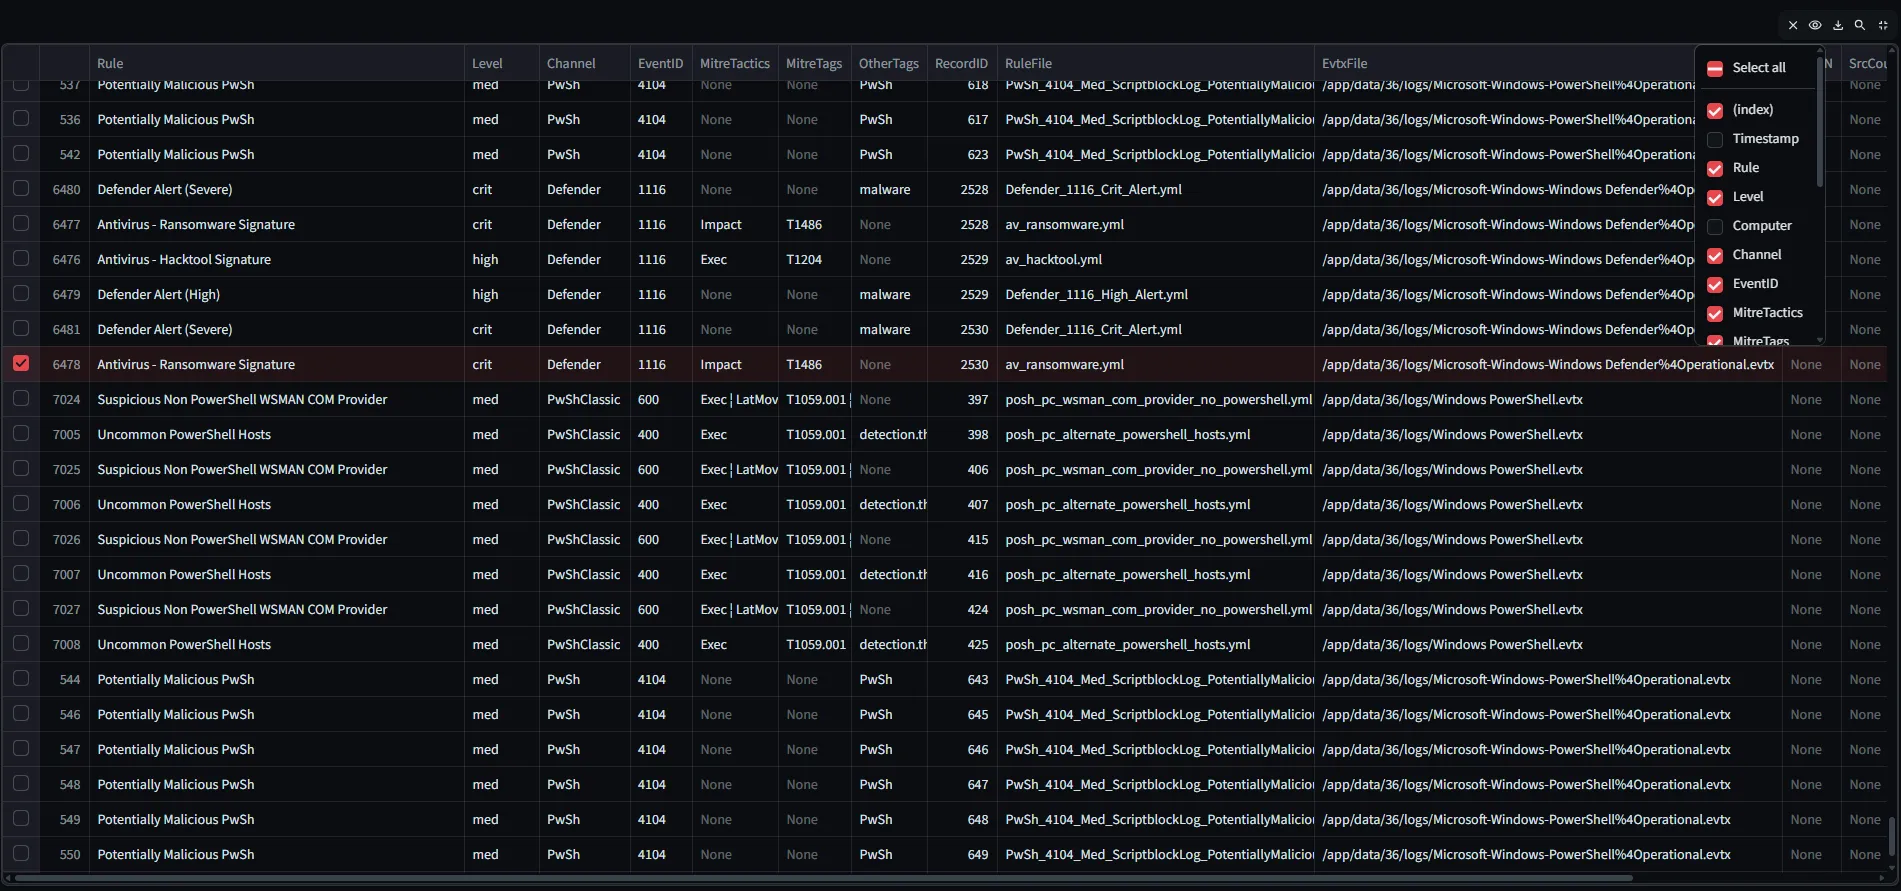
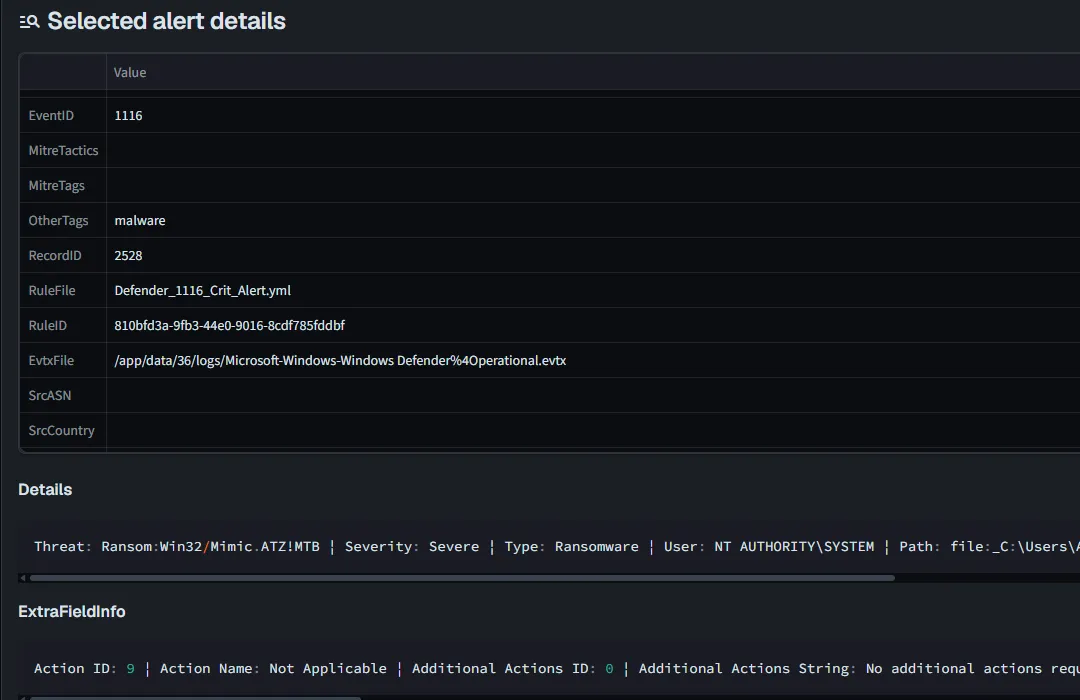
- Rust-based EVTX engine. Sigma rules, MITRE ATT&CK mapping, severity scoring and eight selectable analysis profiles.
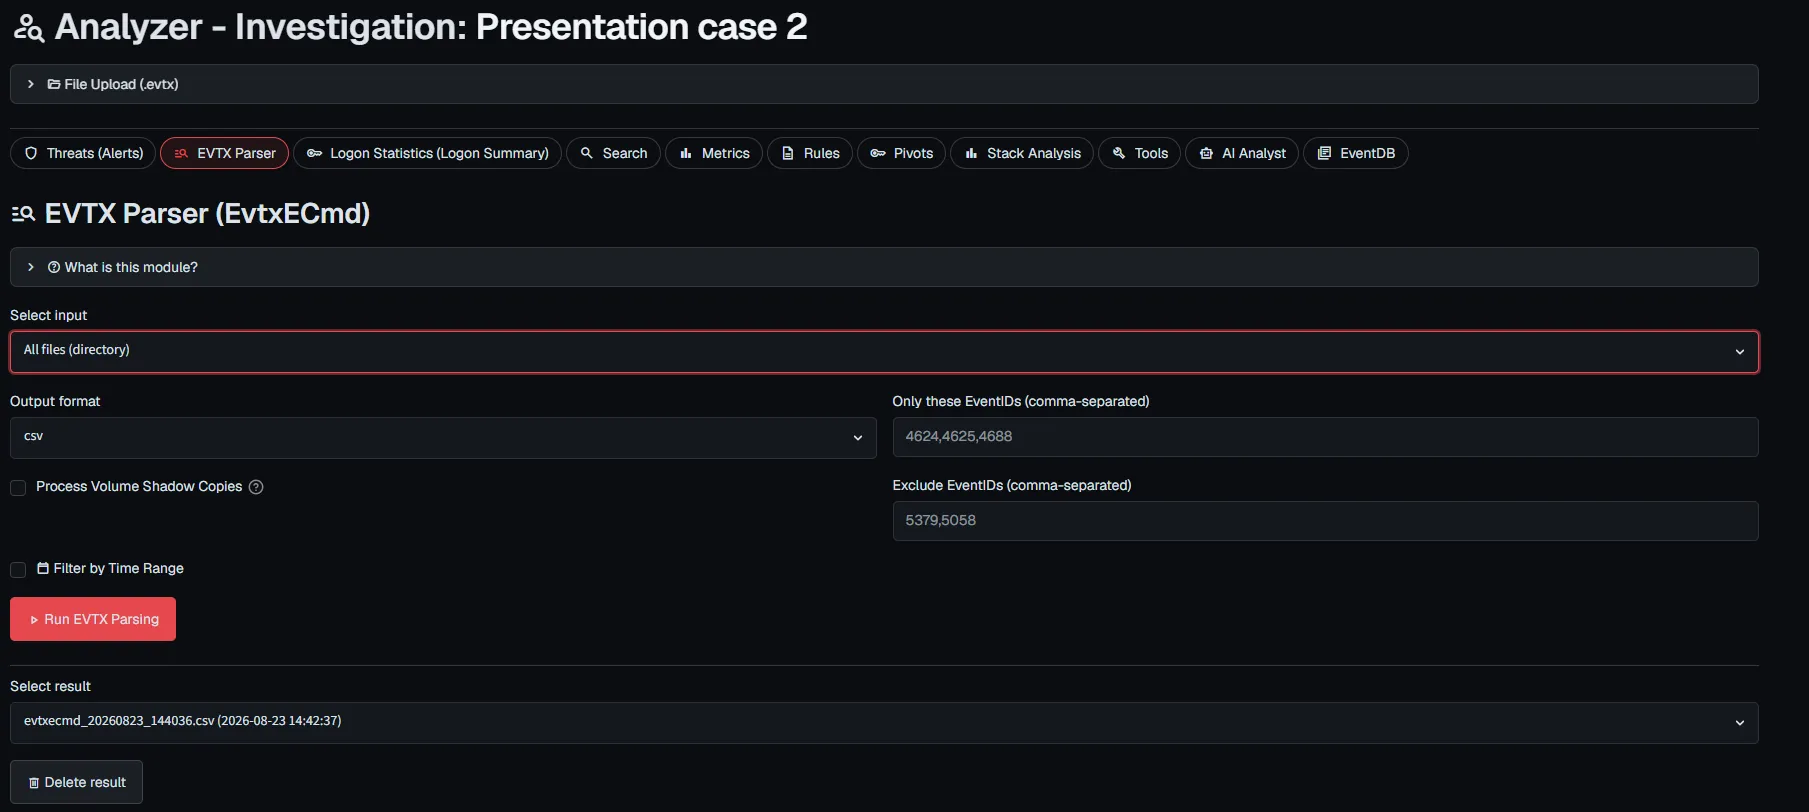
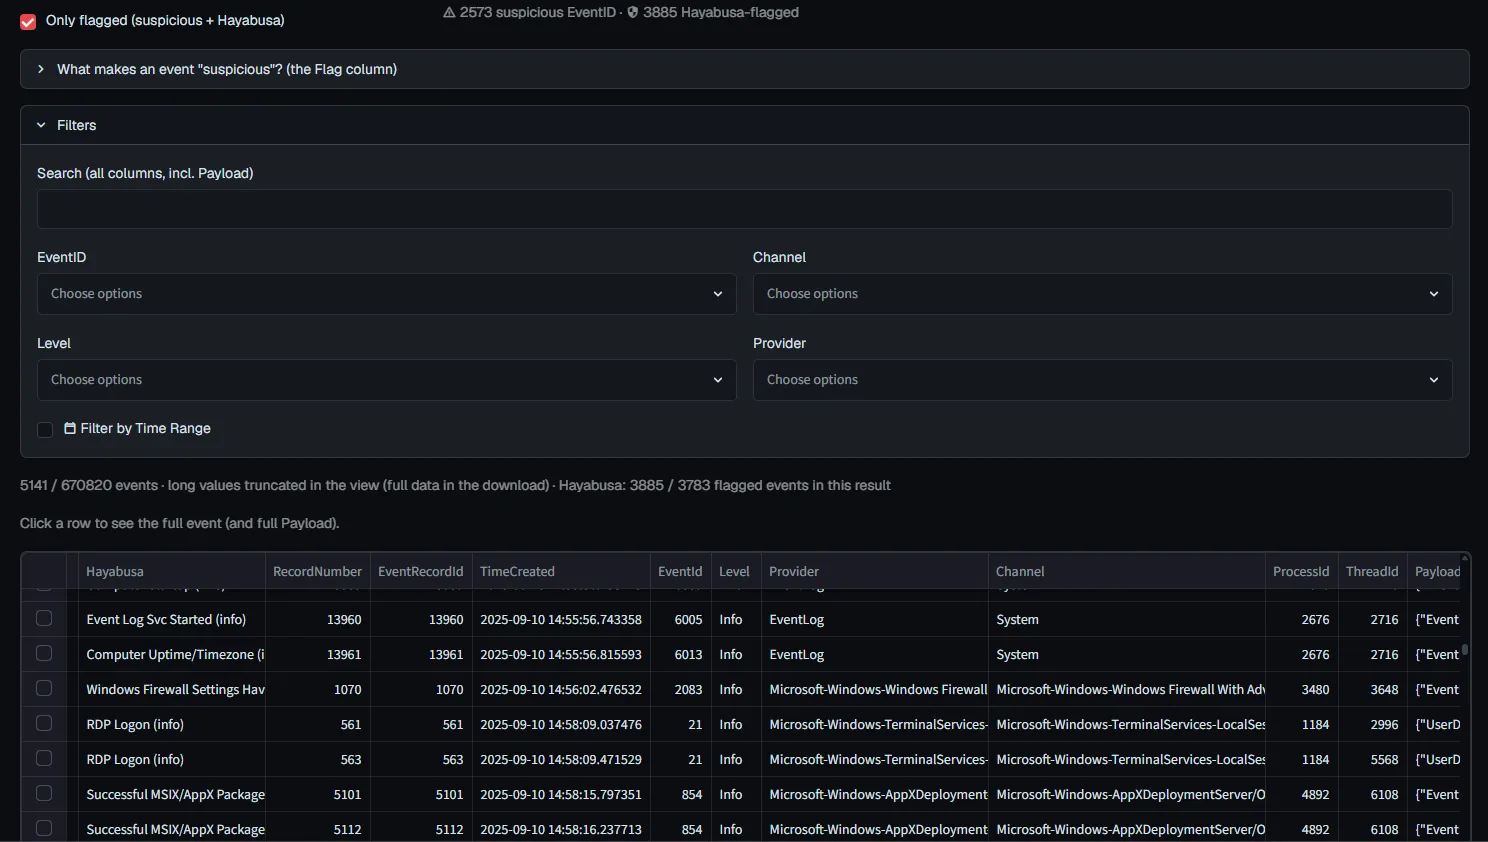
- Full forensic timeline. EvtxECmd parses every event, with five- and thirty-minute pivots on one machine or by account.
- Verified AI investigation (Mecha). Code drives the investigation, the AI rules on closed questions, and 12 coverage gates verify the report.
- Your choice of AI provider. Local Ollama or LM Studio, cloud OpenAI or Claude, and a Chat that queries the timeline itself.
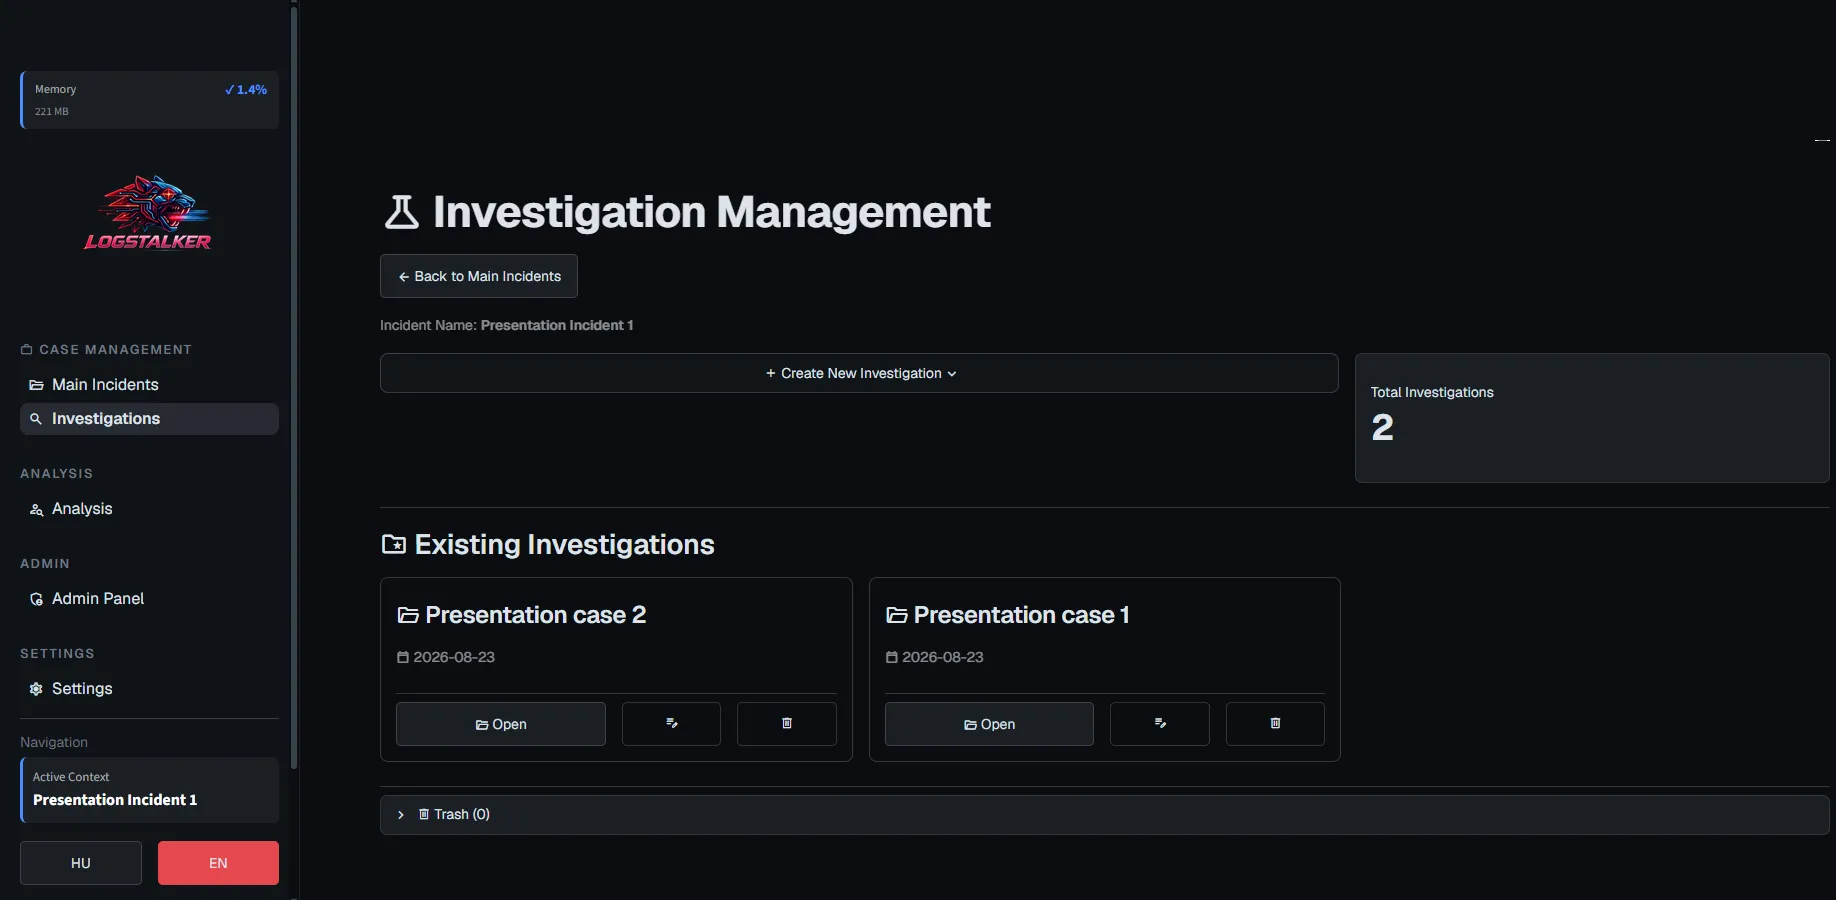
- Three-tier incident management. Main incident, investigation and analysis on PostgreSQL, with RBAC roles and a restorable trash.
- PowerShell ScriptBlock reconstruction. Complete scripts from fragmented events, Base64 decoding and automatic IoC extraction.
- Nine kinds of Stack Analysis. Frequency-based anomaly detection across processes, command lines, services and logons.
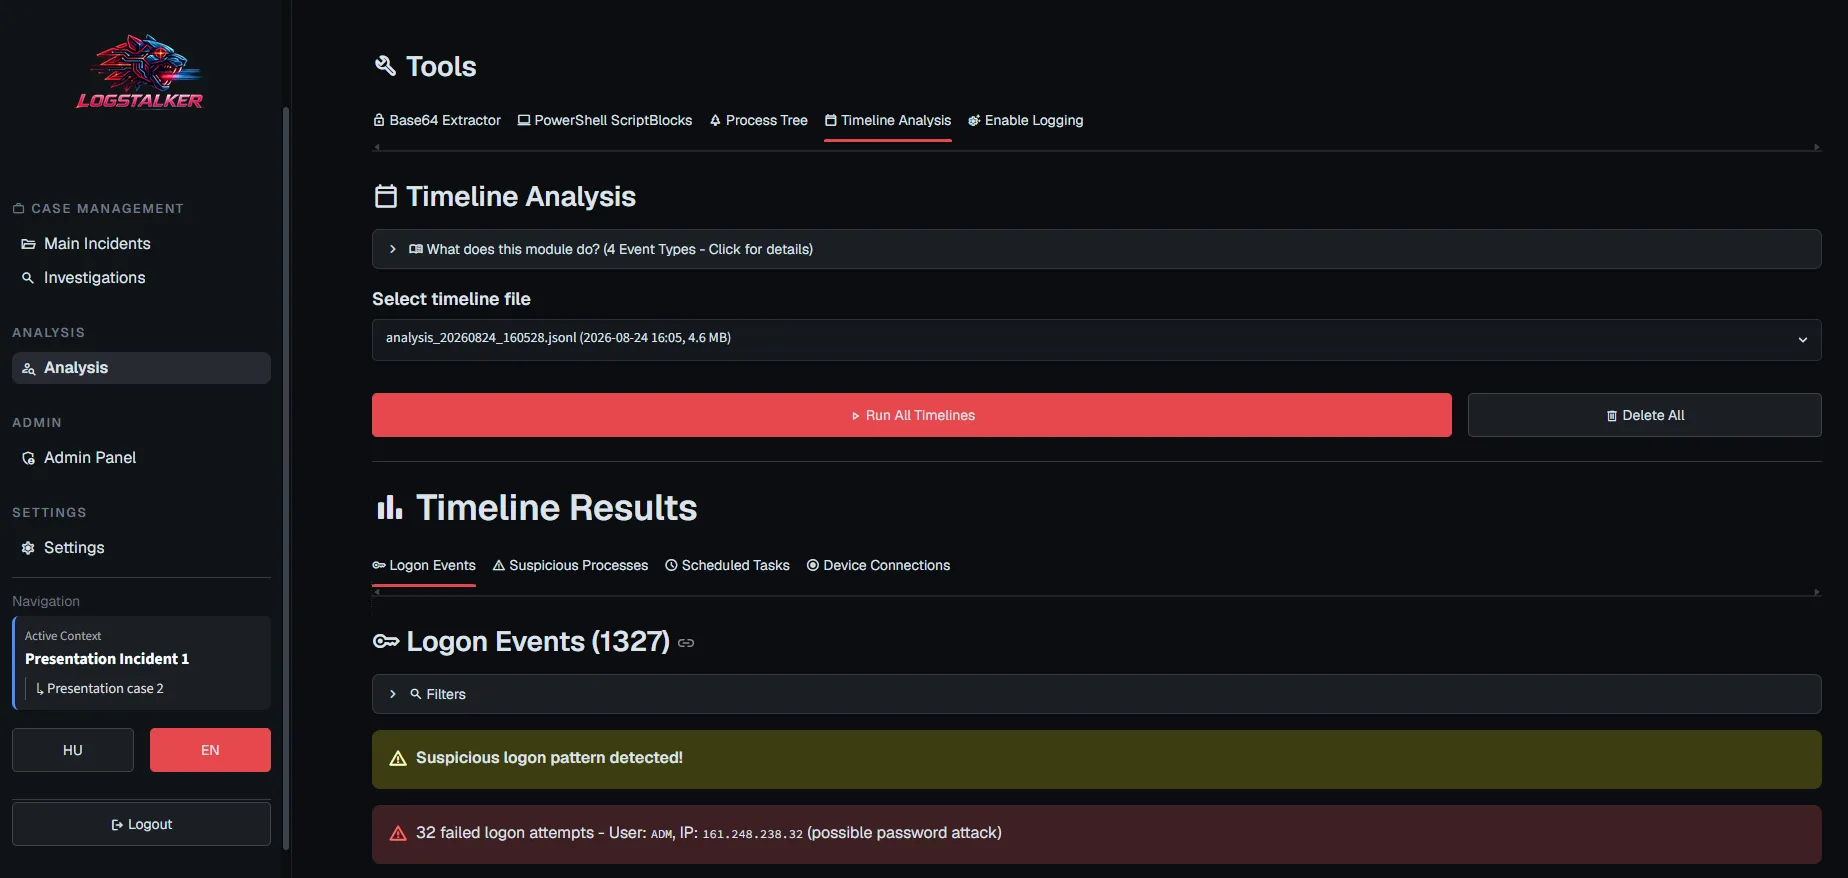
- Four timeline modules and a process tree. Logons, suspicious processes, scheduled tasks, device connections and the parent-child tree.
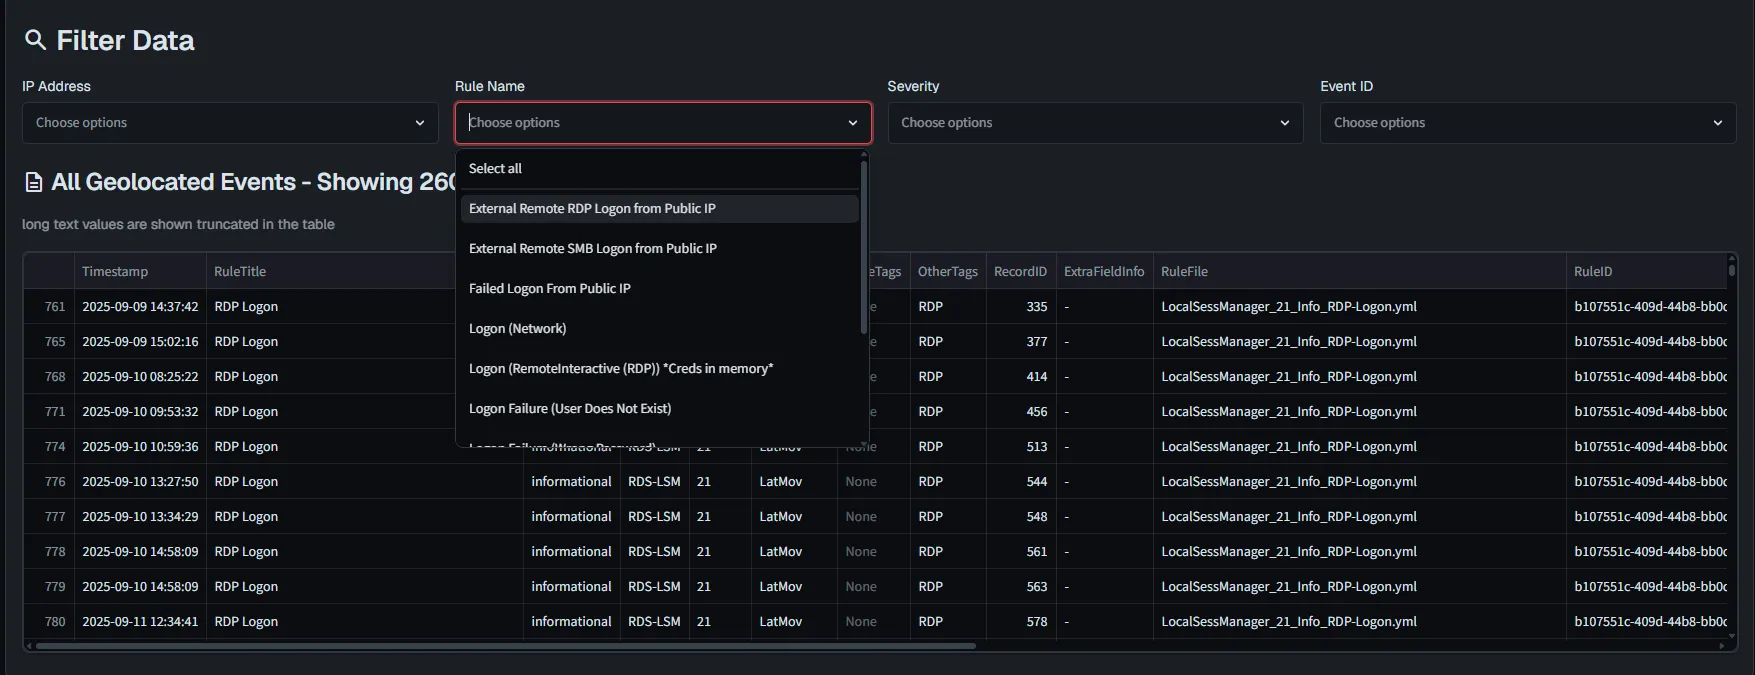
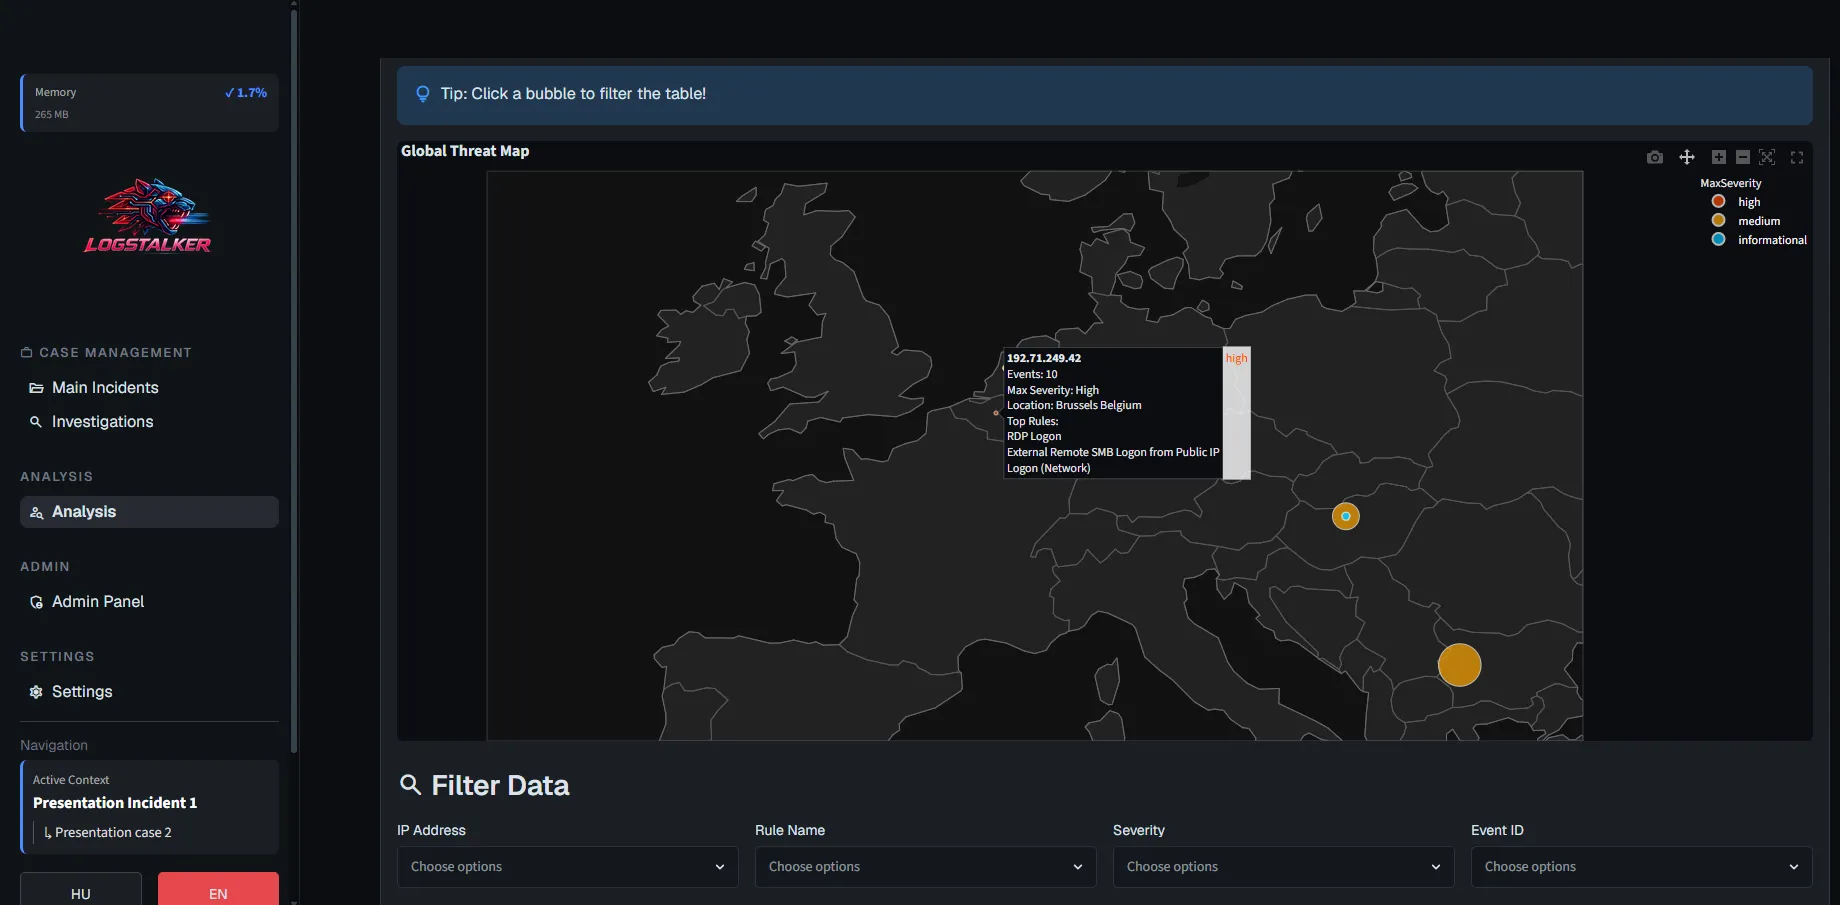
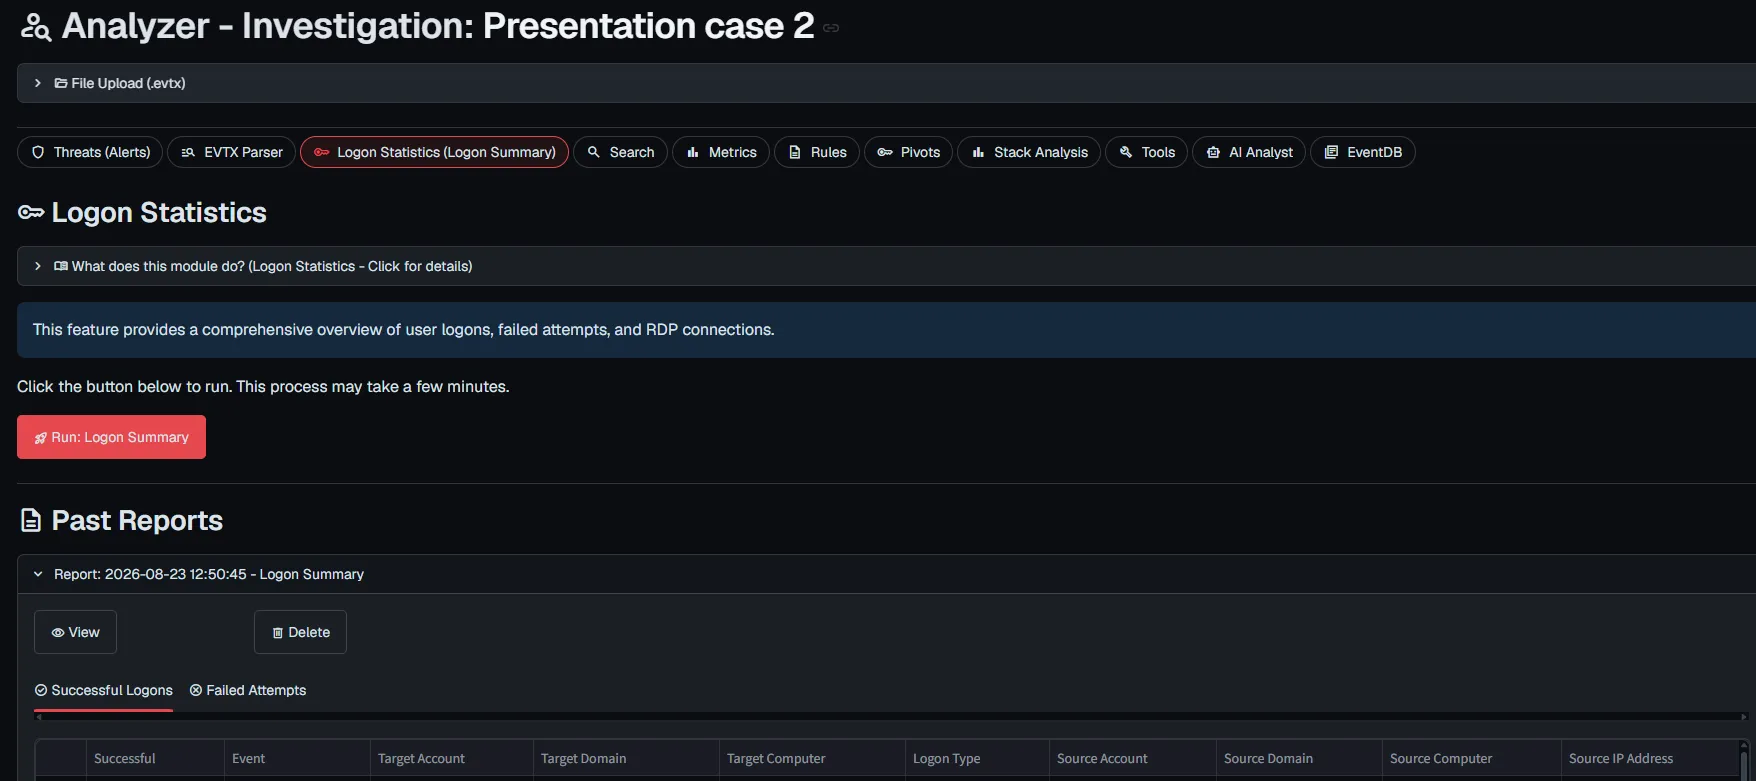
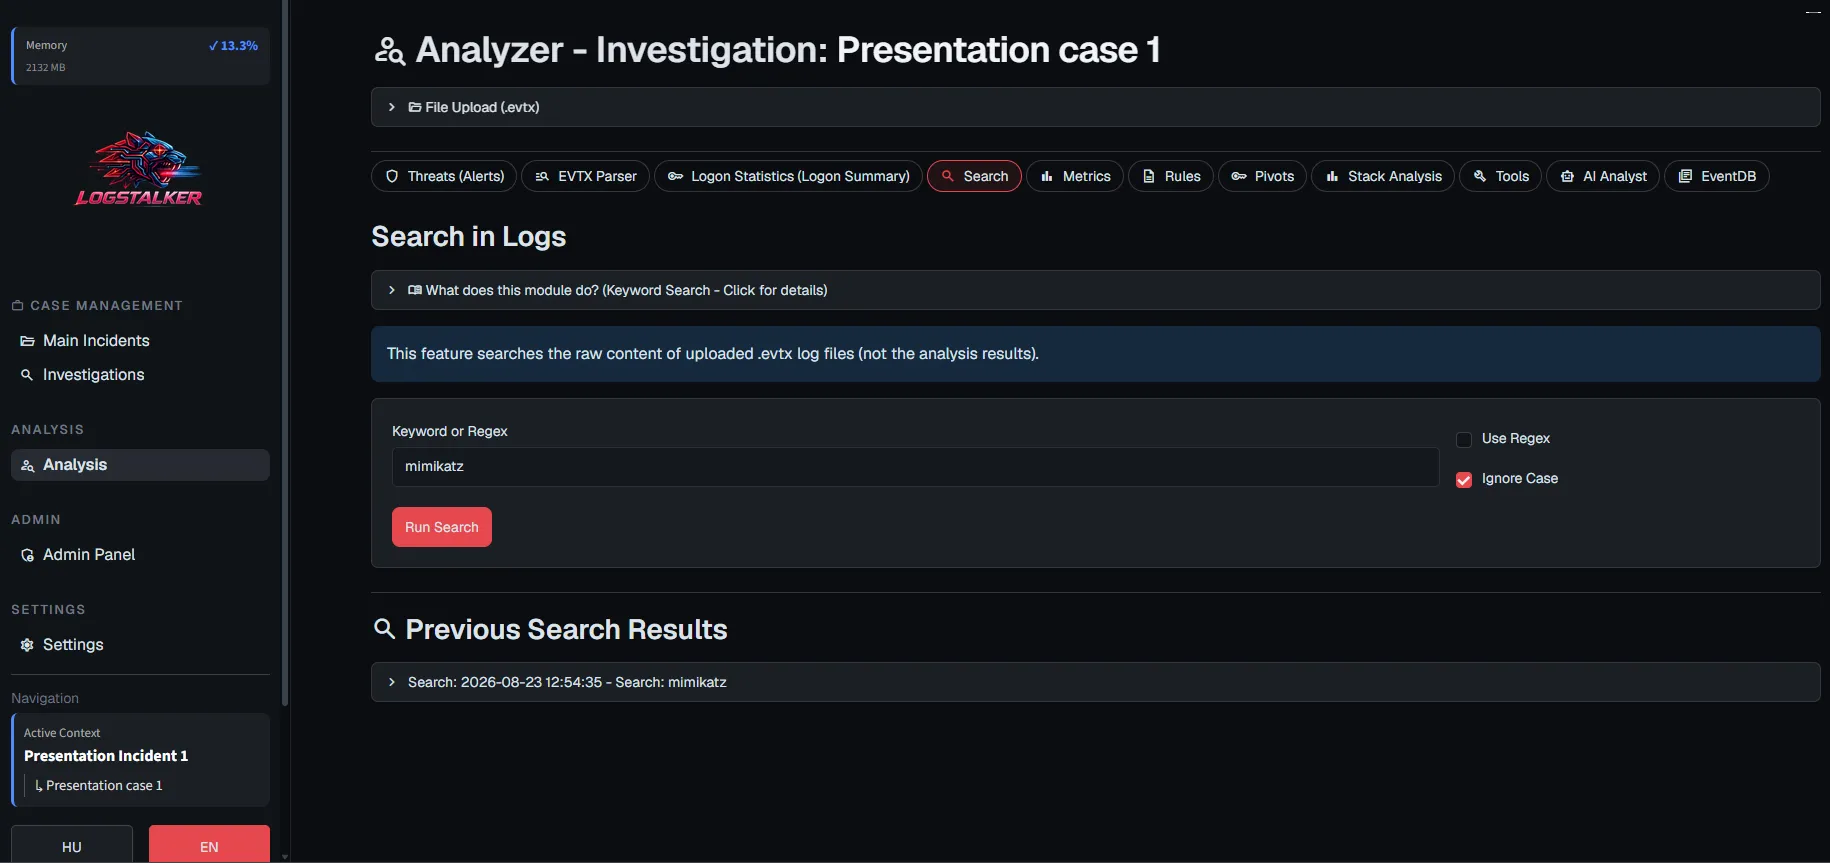
- GeoIP map and VirusTotal checks. Logon Summary, regex log search and lateral movement pivots with interactive visualizations.
- Incident report and custom rules. Printable HTML and PDF report, custom Sigma rules checked before saving, a self-updating rule set.
- Logging coverage. EventID metrics, the OSSEM event dictionary and a downloadable script that turns on endpoint logging.
- Security by default. HTTPS, bcrypt authentication, an encrypted key store, a full audit log and offline annual licensing.
> SCREENSHOTS
What it looks like in practice