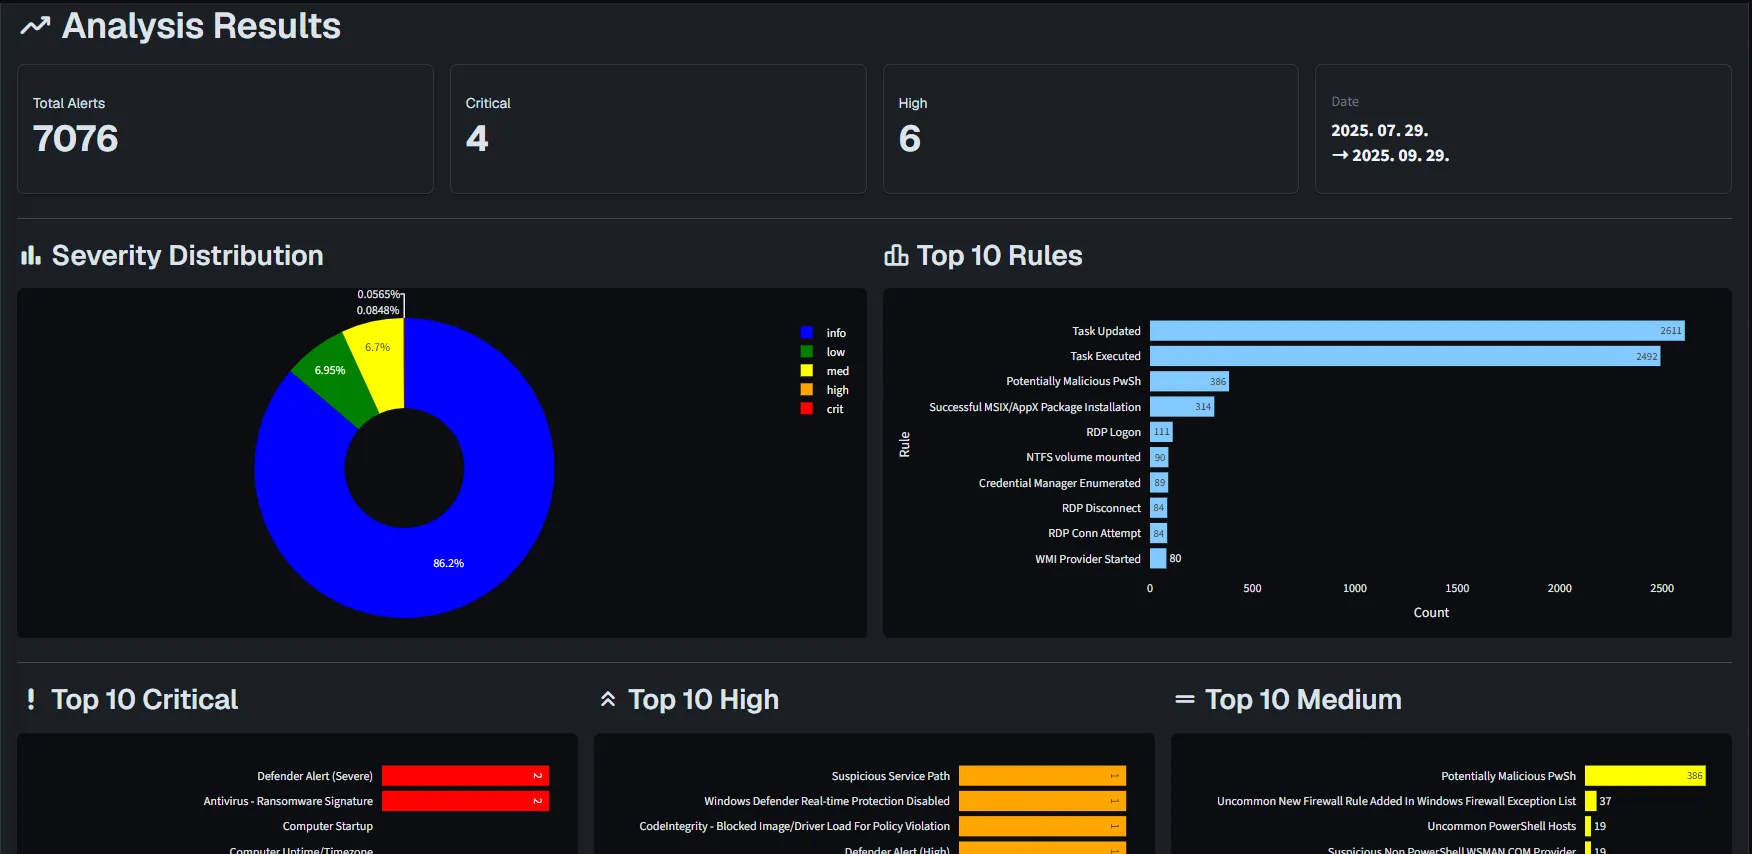
LogStalker
Rapid investigation of event logs from compromised or suspicious Windows workstations and servers.
[ SELF-HOSTED CYBERSECURITY ]
For prevention and post-incident investigation: fast, reliable analysis on your own server.
// PRINCIPLE_01
Event logs, suspicious files, emails: your most sensitive data is analyzed on your own server. External lookups (VirusTotal, AbuseIPDB) run only if you turn them on.
// PRINCIPLE_02
Work faster and more effectively: the tools handle the routine work, so the analyst only has to evaluate the results.
// PRINCIPLE_03
It works for a one-person IT team just as well as for a full analyst team: it runs on a single server and fits into the workflows of a large SOC.
> PRODUCT SUITE
Focused tools for four critical areas: Windows event logs, suspicious files, phishing emails and web server logs.
Rapid investigation of event logs from compromised or suspicious Windows workstations and servers.

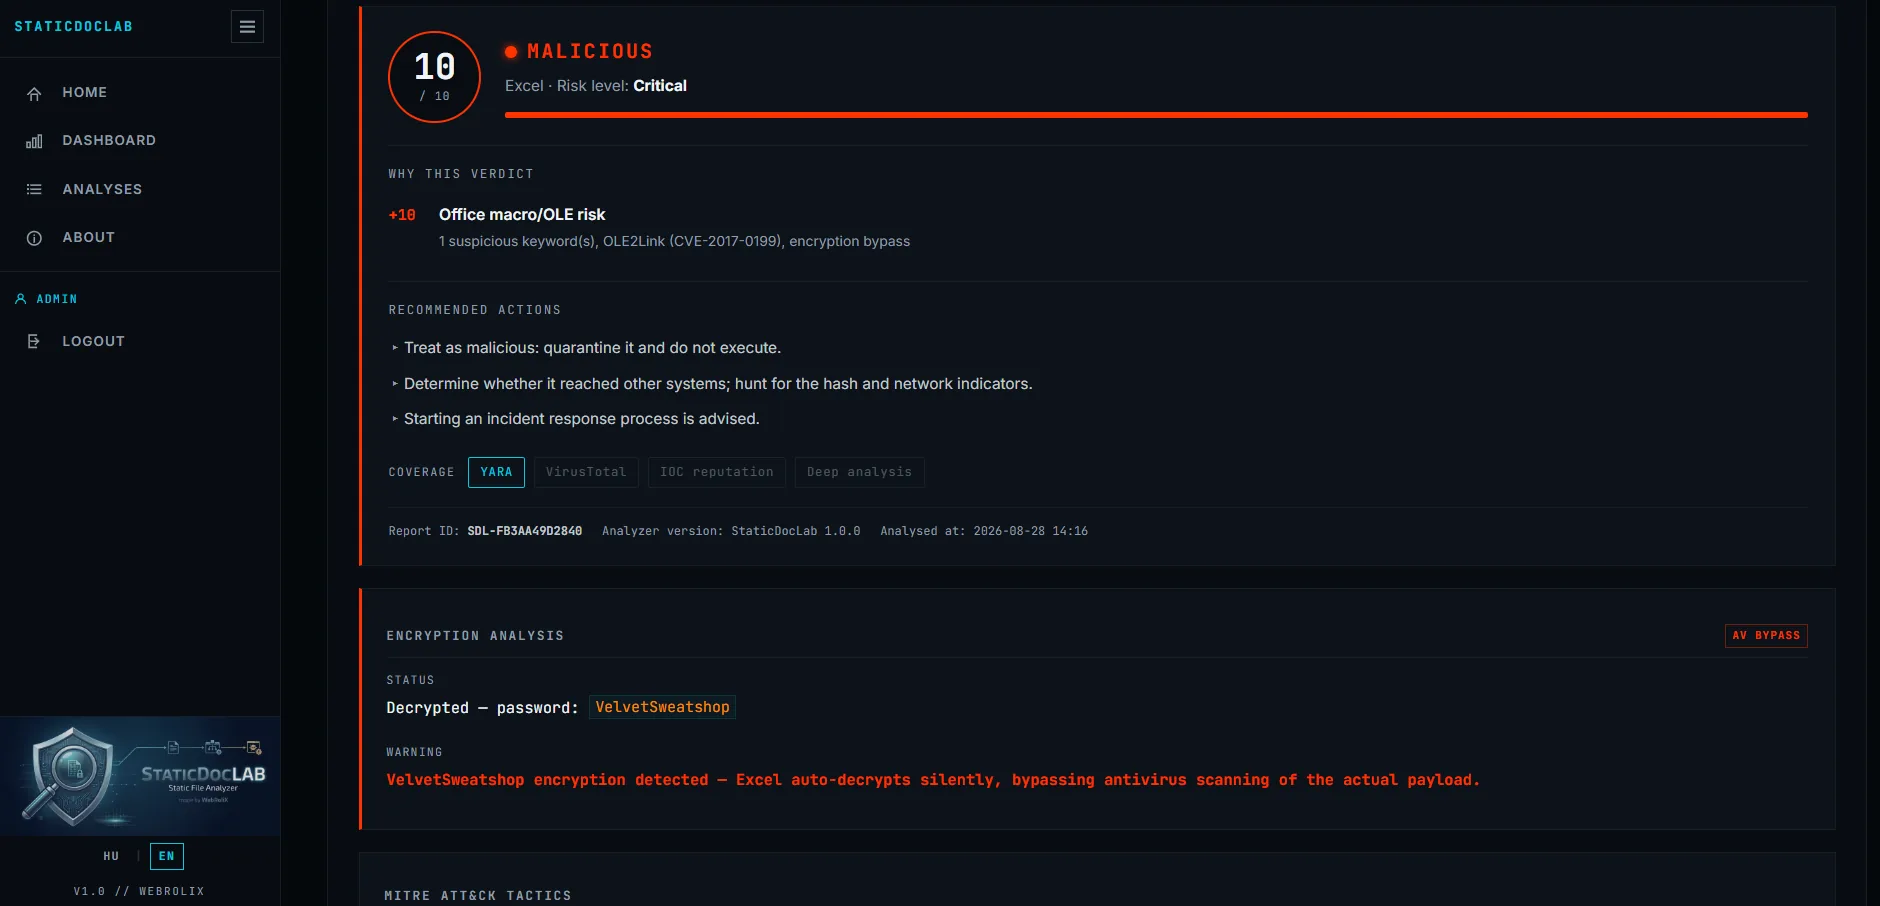
Fast static analysis of the files you receive every day. An extra line of defense, no sandbox, on your own infrastructure.
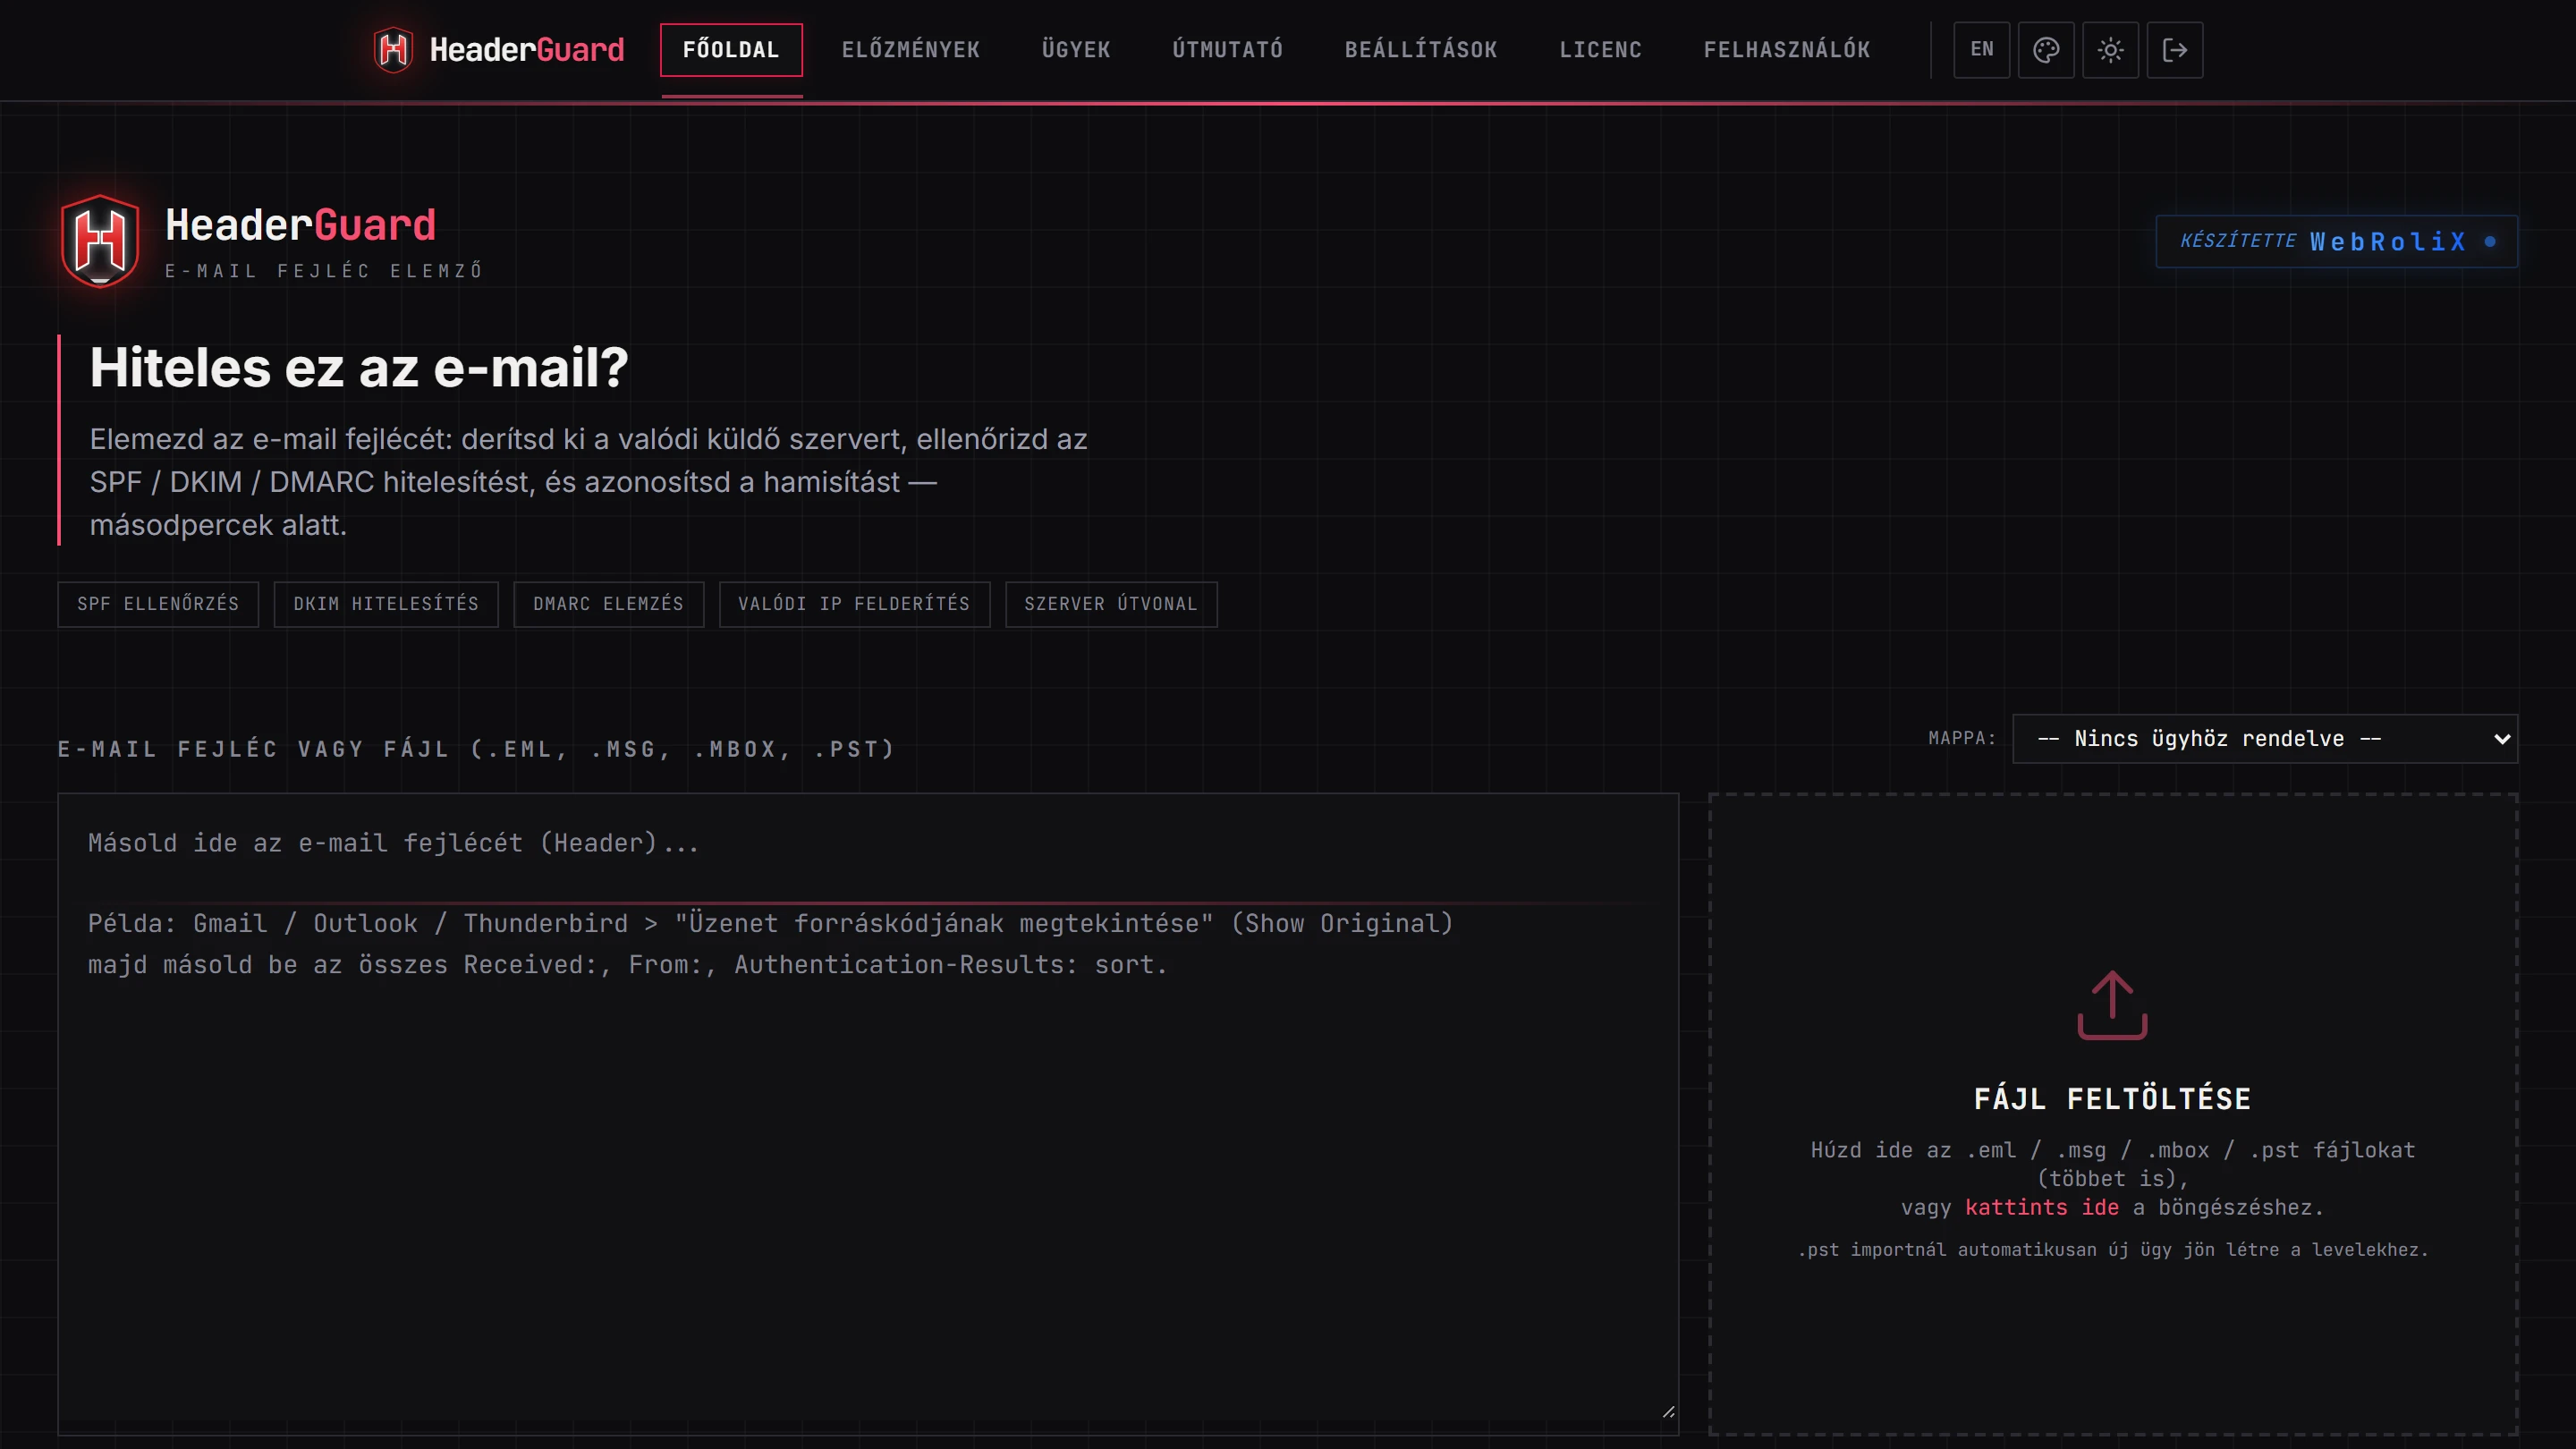
The full email or just the header from your email client: comprehensive phishing analysis with threat intelligence integration and campaign-level correlation.

Fast web server access log analysis: line-by-line streaming ingestion, pre-aggregated queries, visual trends and actionable insights.
> WHAT IT LOOKS LIKE
One screen from each of the four products, exactly as it will run on your own server.
> DEPLOYMENT
Docker Compose on your own server: pull, set up the .env file and start it. Running in under ten minutes.
Annual license key delivered securely. Access for your chosen user tier activates instantly.
Run as many investigations as you like. The data stays on your own hardware, and we never see it.
// READY TO DEPLOY?
Request a live demo, or tell us what you are protecting and we will help you pick the right tool.